AI-assisted threat detection · OT security · configuration assurance · attack surface
Security infrastructure,
made operable.
Network memory and threat detection, configuration assurance, and attack-surface intelligence — three products on one platform, running entirely on your own appliance. Built for the teams that run banks, utilities and critical infrastructure.
- 100% on-prem · air-gap
- 50+ vendors, agentless
- IT + OT on one sensor
- London · İstanbul
OT segment · Purdue · Seraxi Relay
L3 → L1 · boundary crossing
TDS event stream
- 13:16:53 HIGH Modbus write · FC16 eng-ws-12 → PLC-07 (S7-1500) · outside change window
- 13:16:41 MED DNS tunnelling host-11 → *.sync-cdn.example · entropy 4.7
- 13:16:22 CRIT C2 beacon 192.168.40.23 → external · TLS 443 · 60s period
- 13:15:58 INFO New OT asset Rockwell CompactLogix · L1 · EtherNet/IP
- 13:15:30 MED Lateral movement SMB admin share · 192.168.12.7 → 3 hosts
Verdict: Unauthorized Modbus write to PLC-07 from an engineering workstation. 3 signals fused: IDS rule (FC16), behavioural ML deviation, Purdue boundary crossing L3→L1.
OT segment · Purdue
L3 → L1 · boundary crossing
OT event stream · passive
- 13:16:53 HIGH Modbus write · FC16 eng-ws-12 → PLC-07 (S7-1500) · outside change window
- 13:16:10 HIGH DNP3 cold restart hmi-02 → rtu-3 · unauthorised source
- 13:15:58 INFO New asset · L1 Rockwell CompactLogix · EtherNet/IP · auto-classified
- 13:15:22 MED Firmware download S7comm · PLC-03 · outside maintenance window
- 13:14:48 MED IT → OT session RDP · 192.168.20.14 → hmi-02 · L3 → L2
Verdict: Write to PLC-07 and cold restart of rtu-3 came from the same engineering workstation, 43 s apart. Not expected process behaviour; the Purdue L3→L1 boundary was crossed twice. Raw packets are in Trace Analysis.
Policy checks · 142 devices
- ✓ No default SNMP community
- ✓ Telnet / SSHv1 disabled
- ! TLS ≥ 1.2 on management 2
- ! Certificate > 30 days 7
- ✓ Firmware not end-of-support
- ✕ No open critical CVE 3
- 3 devices out of policy · advisory matched
Advisory → inventory match
- 22:04 NEW Advisory published FortiOS SSL-VPN · CVSS 9.8 · pre-auth RCE · fixed in 7.2.10
- 22:05 HIT edge-fw-01 · FortiGate 600F 7.2.7 · internet-facing · AFFECTED
- 22:05 OK dc-fw-02 · FortiGate 200F 7.4.3 · not affected
- 22:05 HIT br-fw-07 · FortiGate 60F 7.0.12 · VPN enabled · AFFECTED
- 22:05 HIT vpn-fw-04 · FortiGate 100F 7.2.6 · AFFECTED · backup verified 21:40
Result: 3 of 142 devices affected, 2 internet-facing. Recommended fix: upgrade to 7.2.10. Change window 02:00; signed baseline ready for rollback.
External scan · live
1 critical path · fix first
From open port to the app behind it
- hop 0 NET api.bank.example:8443 open from the internet · TLS 1.2 · cert 19 days left
- hop 1 F5 vs_api_443 · BIG-IP SNAT · pool pool_api
- hop 2 APP 10.10.113.11:8080 sg_auth_backend · Java 17 · Log4j 2.14
- hop 3 CVE CVE-2021-44228 · KEV EPSS 0.97 · reachable from the internet
- + AI Shadow AI ollama · 10.10.113.40:11434 · unauthenticated
Priority: Critical path: internet → F5 → auth backend → Log4Shell. Blast radius 3 applications. Nessus and Qualys findings are bound to the same asset; fix this one first.
What it answers
The questions that arrive at the worst possible time.
A FortiOS advisory was published last night. Which of our devices are affected?
Keep matches the advisory to the model and firmware of every device in your inventory and lists the affected ones — in minutes, from real data, not a spreadsheet.
Open productWe think something happened on the network last night. All we have is the firewall's accept/deny log.
Trace kept the packets. Replay the hour on Trace Analysis, or hand the PCAP to incident response.
Open productThe internet sees port 8443 open on us. Which internal application is behind it?
Lens draws the path from the exposed port to the exact internal service on one graph, and scores it by blast radius.
Open productA PLC on the plant floor just took a write from an engineering workstation. Was that supposed to happen?
Relay knows the Purdue level, the protocol and the change window; the write is flagged in seconds and the packets are kept.
Open productThree products. One operating picture.
Each stands alone. Together they close the loop from the wire, to the device, to the internet edge.
Chapter 01 — Seraxi Keep
Configuration assurance for network & security devices
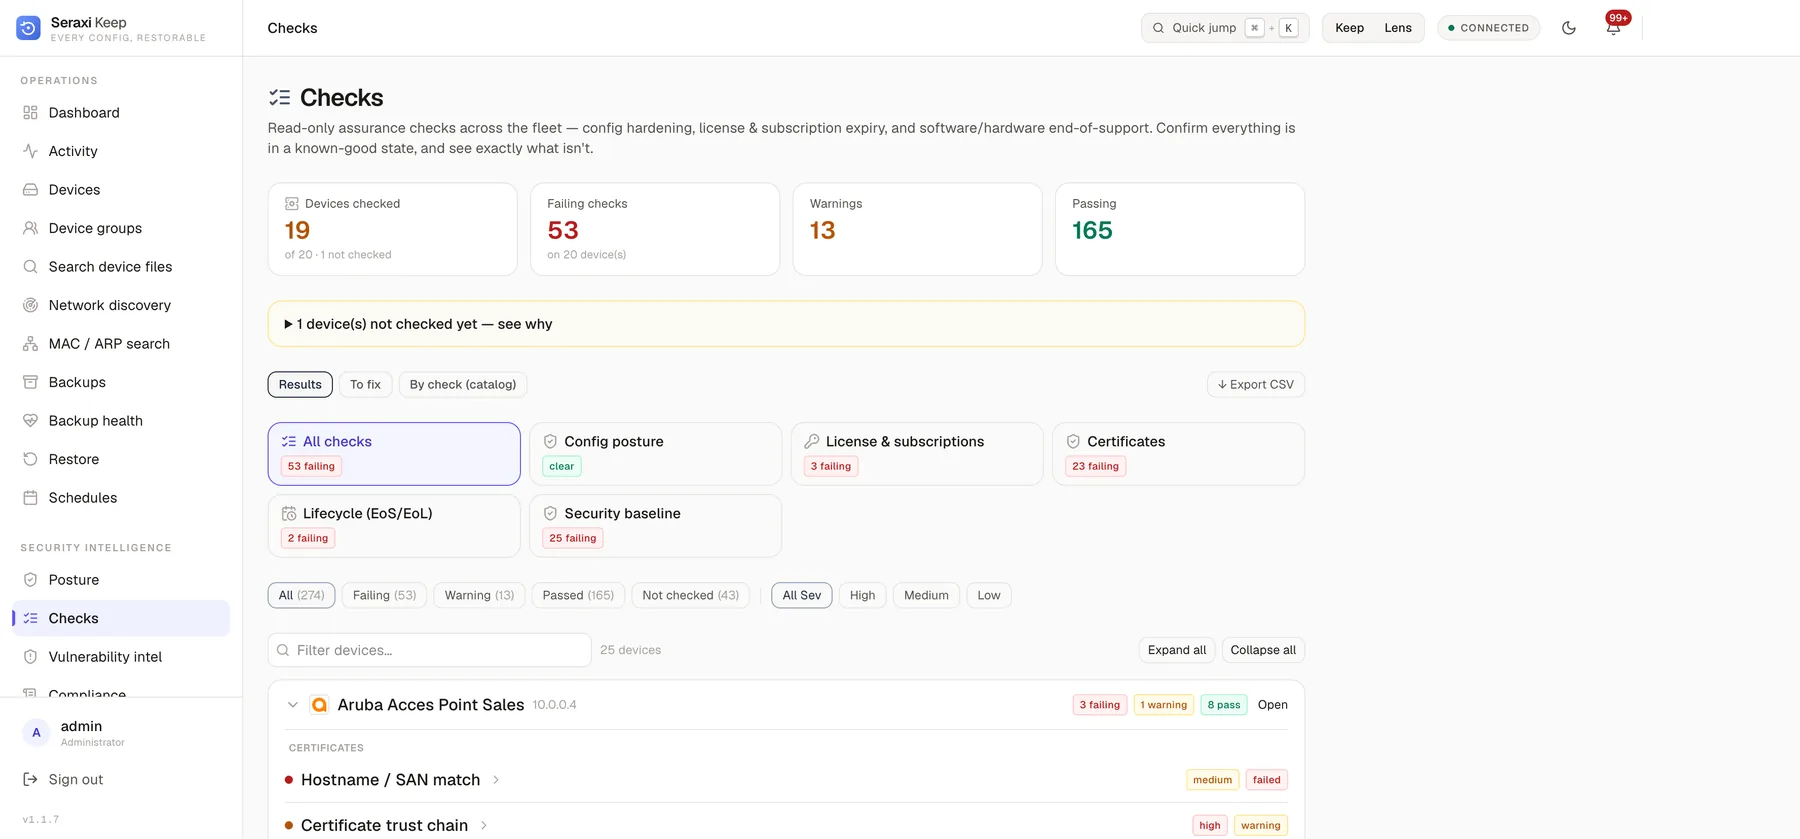
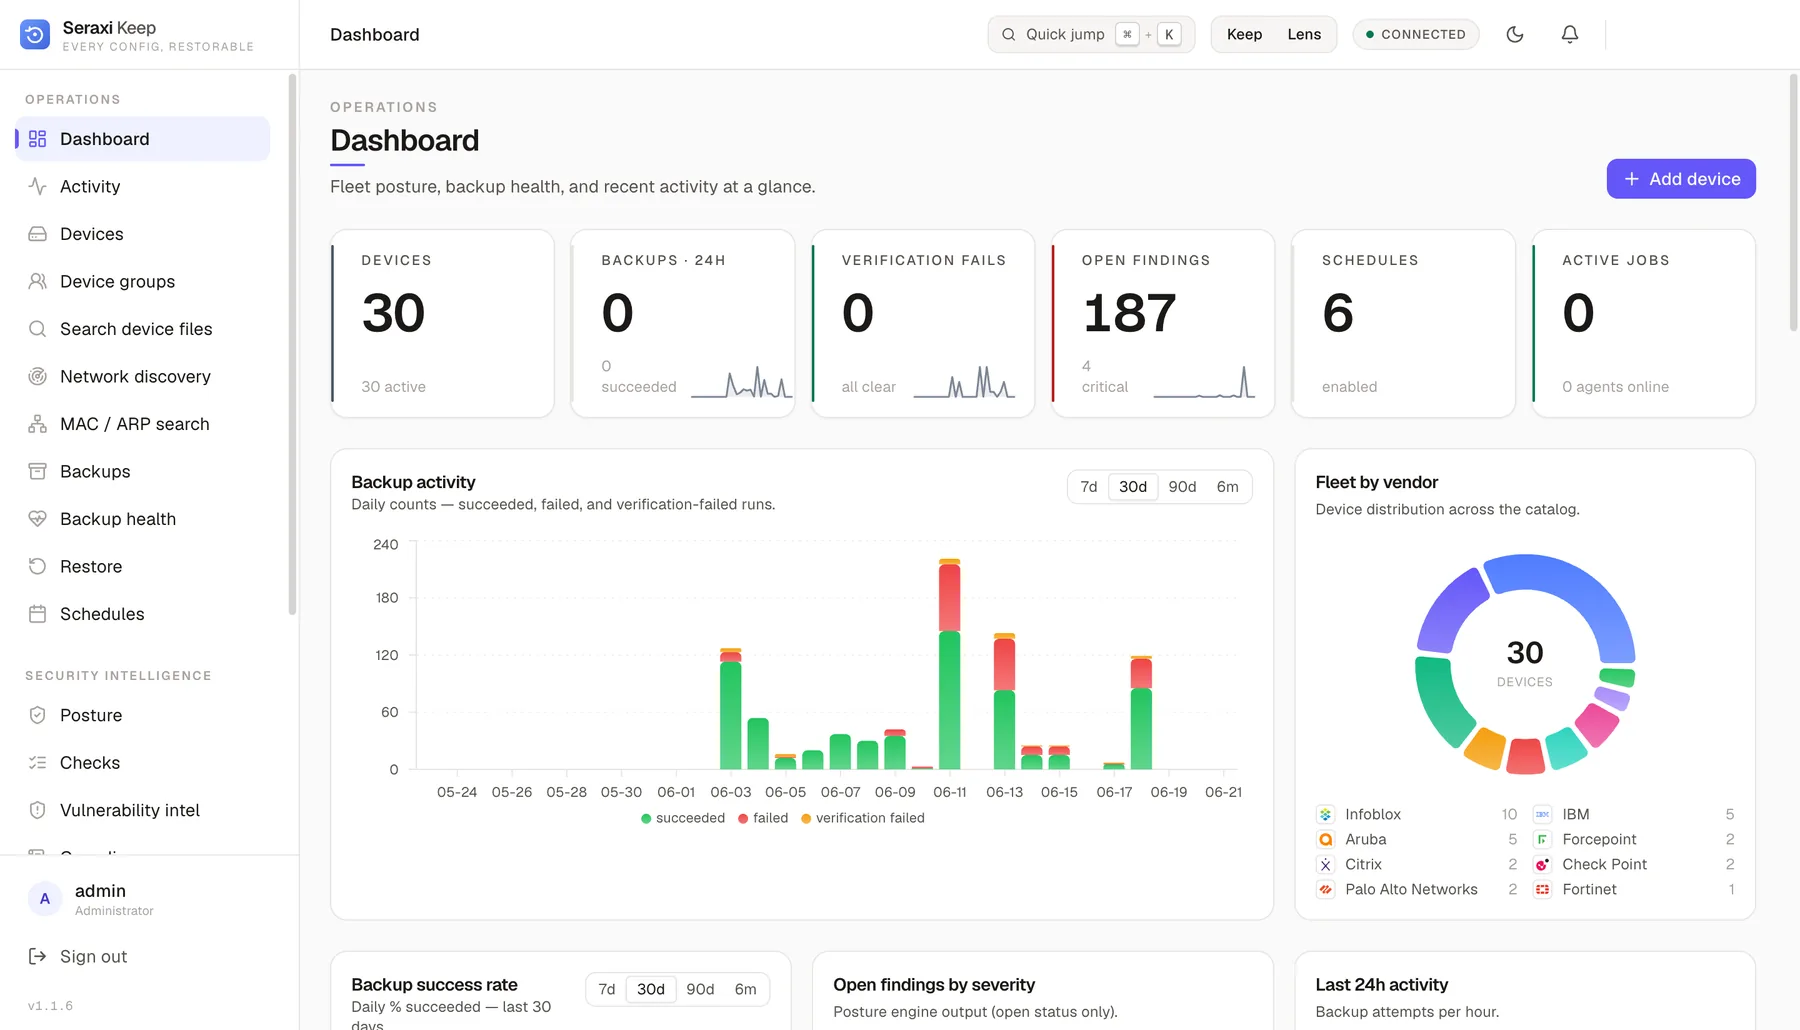
Keep connects to every firewall, router, switch and load balancer you run and keeps a verified baseline of each one. From that baseline it answers the questions that matter: which devices does last night's advisory hit, which configs drift from corporate policy, which certificates expire this quarter, what goes end-of-support next year — and whether the backup would actually restore.
Capabilities
- Advisory-to-device matching
- Configuration baseline & policy controls
- Compliance checks
- Lifecycle: EOL / EOS check
What it answers
- A FortiOS advisory was published last night. Which of our devices are affected?
- Keep matches the advisory to model and firmware across the inventory and lists them — with the recommended fix.
- Does every firewall comply with our security policy?
- Policy controls run against each baseline continuously; every deviation is listed by device and control.
Chapter 02 — Seraxi Trace
Network memory and threat detection — one sensor, modular
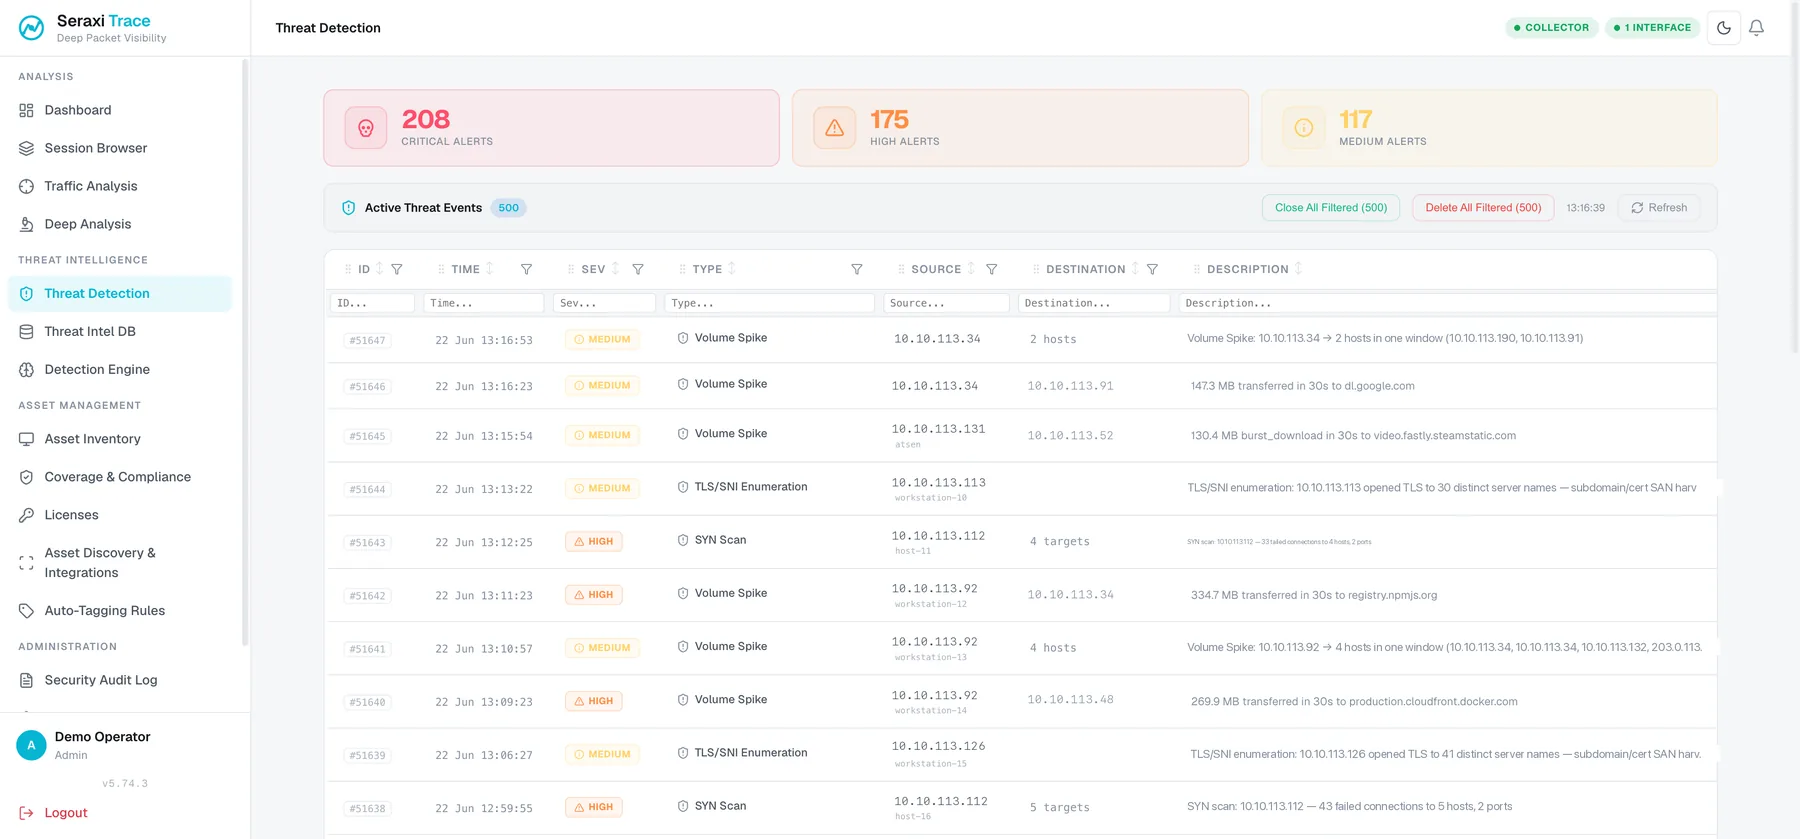
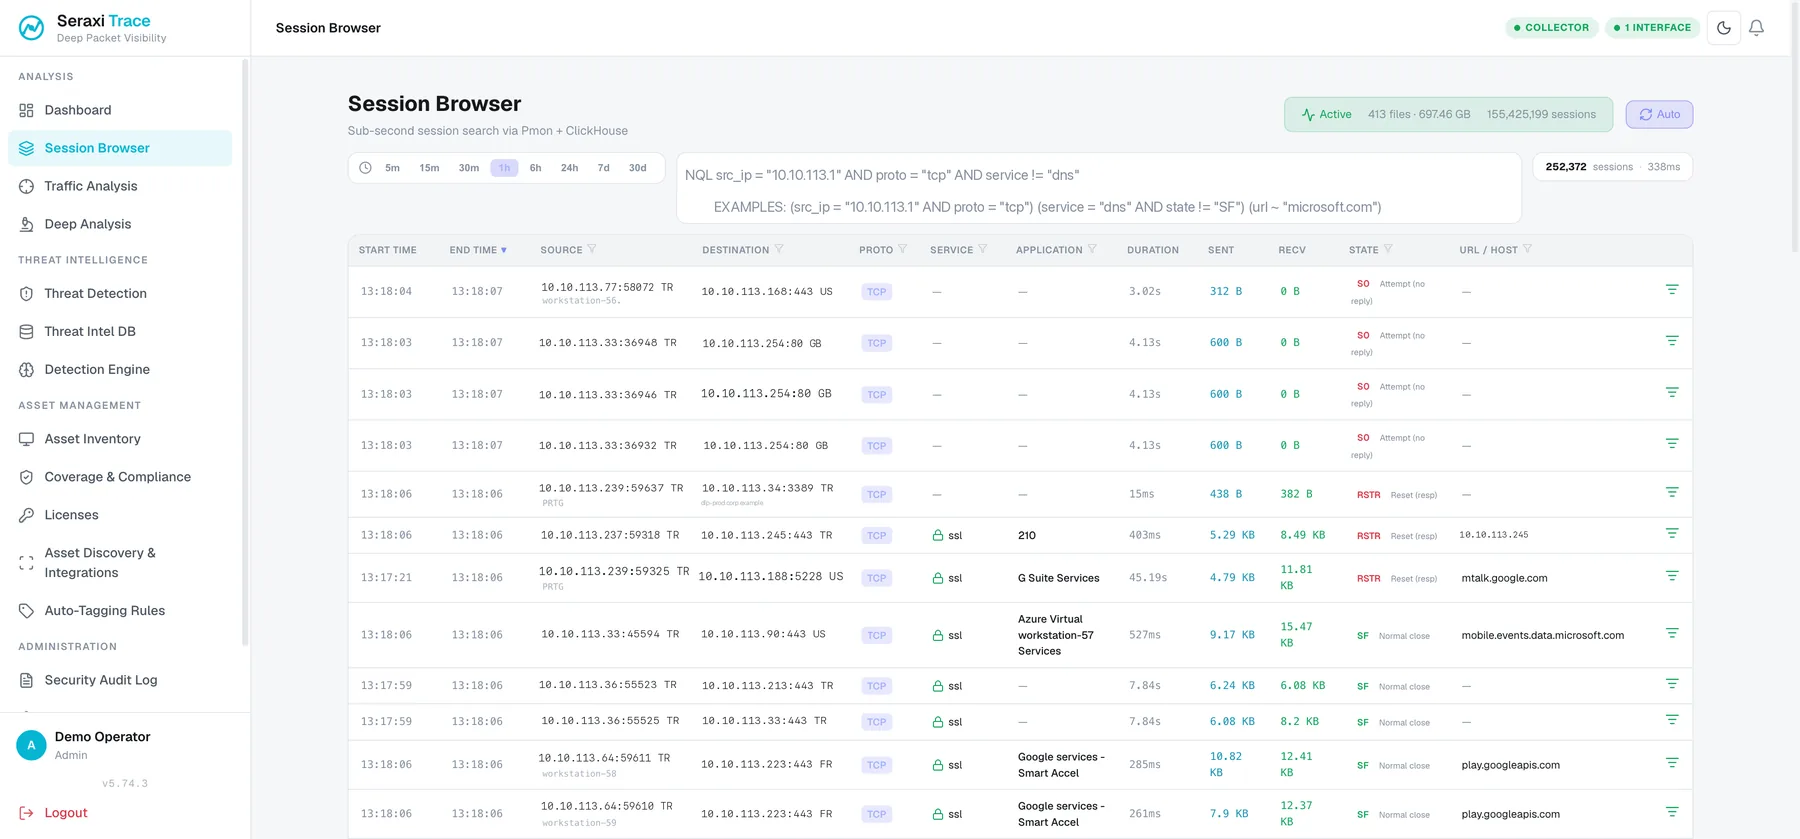
Trace records the raw traffic on your network so an investigation never depends on a firewall's accept/deny log, detects threats with machine learning and a real, self-hosted AI, and brings the same visibility to OT networks — Modbus, DNP3, IEC 104, OPC UA and the PLCs behind them. Underneath, a live asset inventory built from the wire. One appliance; Analysis, TDS and Assets as modules — and Seraxi Relay for OT.
Modules
- Trace Analysis Network memory
- Trace TDS Threat Detection System
- Seraxi Relay OT security · built on Trace
- Trace Assets Inventory from the wire
What it answers
- We suspect an attack happened last night. What do we actually have?
- The packets. Trace Analysis replays the raw traffic for that hour — not a firewall log that only says accept or deny.
- Is something on the network talking to a domain nobody recognises?
- Trace TDS flags the behaviour on live traffic with ML and a self-hosted AI, and shows the packets behind the verdict.
Chapter 03 — Seraxi Relay
OT security that never touches the process
Seraxi Relay is OT security built on the Trace sensor. It listens passively to industrial networks, identifies PLCs, RTUs, HMIs and SCADA servers from the wire, places them on the Purdue model and watches the control traffic itself — Modbus, DNP3, IEC 104, IEC 61850, OPC UA, PROFINET, EtherNet/IP, S7comm — with a self-hosted AI that learns what normal looks like for your process.
Capabilities
- Passive protocol decoding
- Purdue asset map
- Control-traffic baselining
- IT / OT boundary monitoring
What it answers
- A PLC took a write from a workstation. Was that supposed to happen?
- Relay knows the Purdue level, the protocol and the maintenance window; the write is flagged in seconds and the packets are kept.
- What is actually on the plant network — every PLC, RTU, HMI?
- Passive discovery from the wire: vendor, model, firmware and protocol for 50+ device types, placed on the Purdue model automatically.
Chapter 04 — Seraxi Lens
External + internal attack surface, on one graph
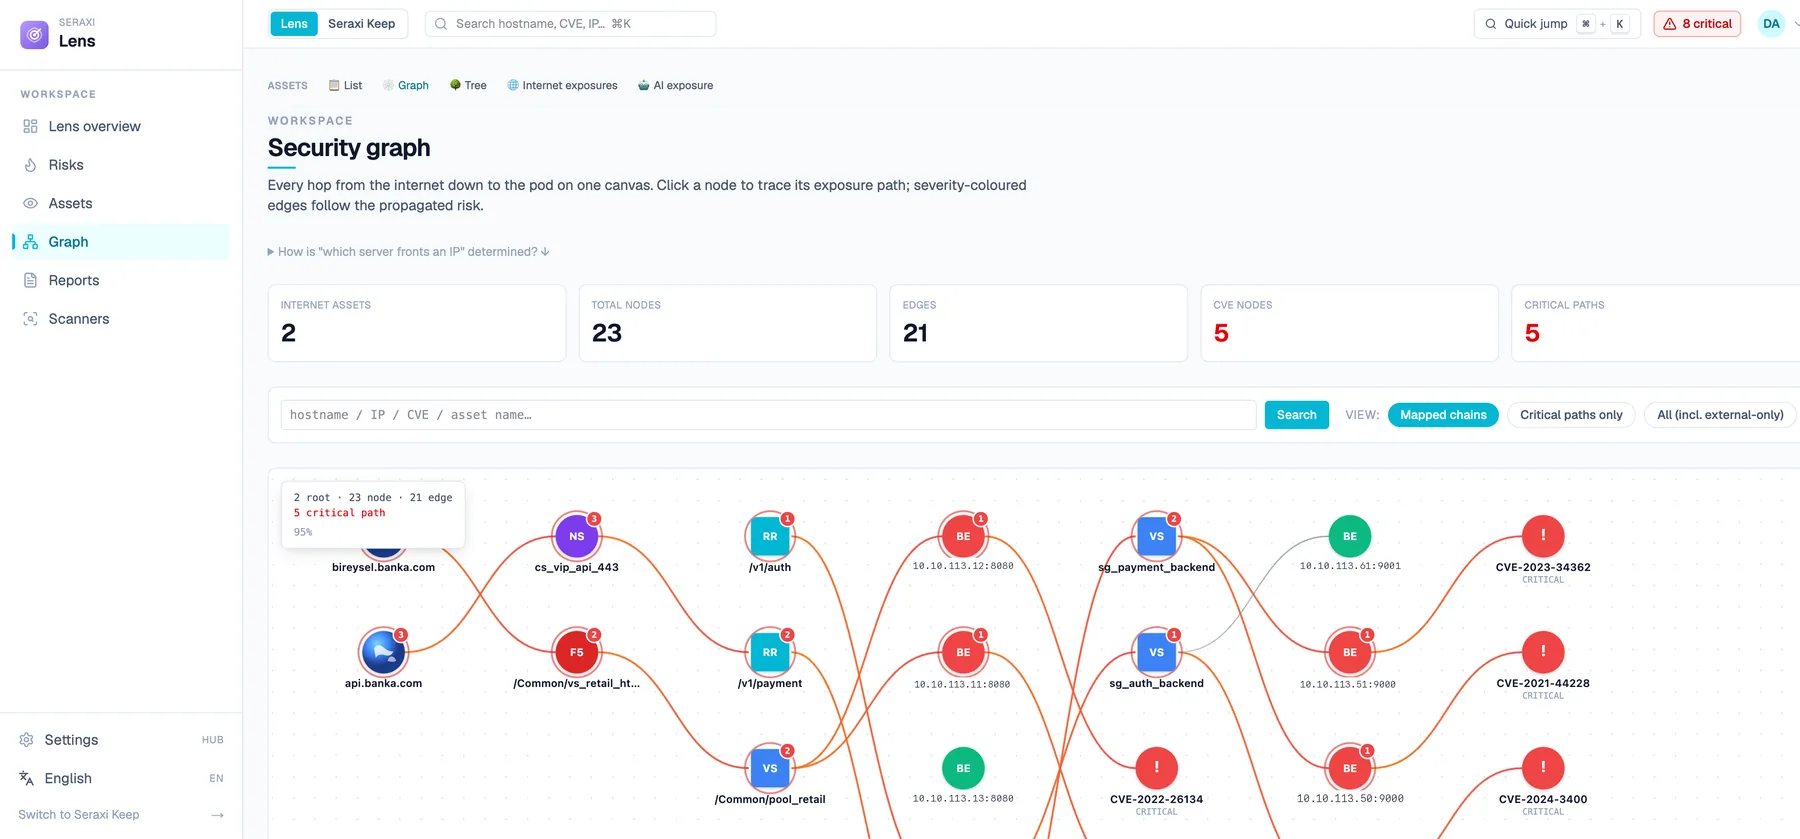
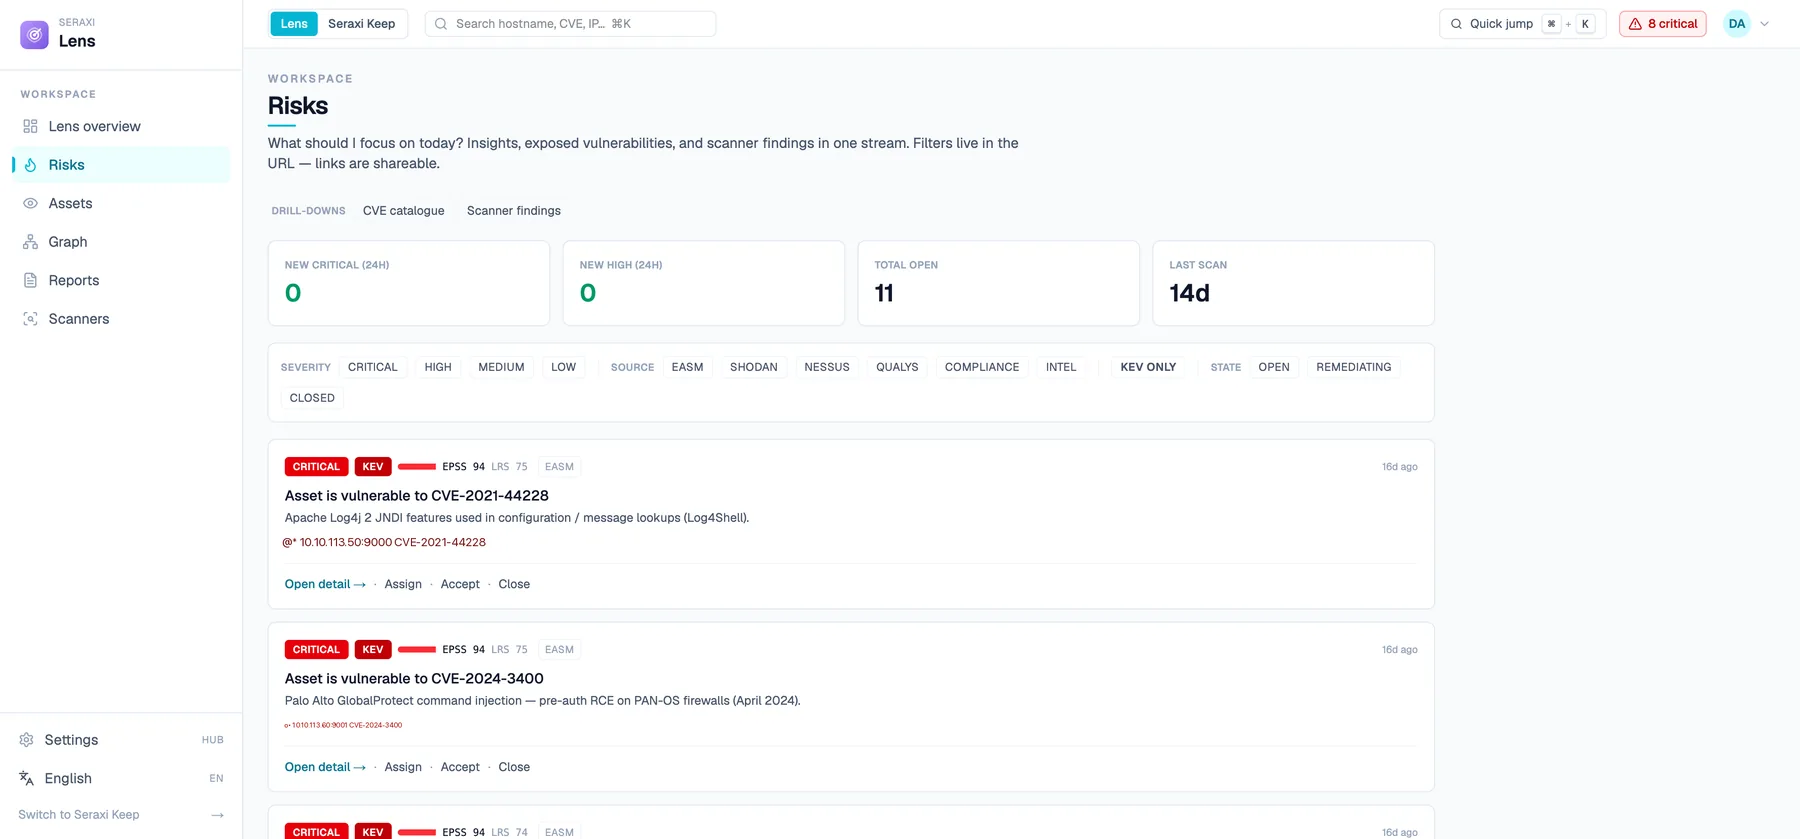
Lens shows how an open port the internet can see reaches the exact internal application behind it — the full outside-in path on one live security graph. A complete EASM platform with its own external scanner built in, it unifies the scanners you already run, scores everything with one Lens Risk Score, and surfaces shadow AI no one registered.
Capabilities
- Outside-in path mapping
- Complete EASM, built-in scanner
- Unifies your scanners
- AI & shadow-AI exposure
What it answers
- The internet sees port 8443 open. Which internal application is behind it?
- Lens draws the path from the exposed port to the exact service on one graph.
- Someone stood up an LLM server. Is it exposed?
- Lens discovers self-hosted model and MCP servers and flags the unauthenticated ones.
Coverage
The vendors you run. The frameworks you answer to.
Vendor-native connectors, no screen-scraping. Controls map to the frameworks your auditors ask about — mapped, not certified.
Vendors & platforms
- Firewalls & NGFW
- Palo Alto · Fortinet · Check Point · Cisco ASA / FTD
- Routing & switching
- Cisco IOS / NX-OS · Juniper Junos · Arista EOS · MikroTik
- SIEM & SOAR
- Splunk · QRadar · Sentinel · Cortex XSOAR
- Load balancers & ADC
- F5 BIG-IP · Citrix ADC · HAProxy · NGINX
- Network sensors
- SPAN / TAP · ERSPAN / GRE · NetFlow / IPFIX · PCAP import
- Attack surface
- Public DNS · Certificate transparency · WHOIS / RDAP · Port & service scans
Frameworks & regulations
- ISO 27001
- PCI DSS
- BDDK
- KVKK
- NIS2
- DORA
- NIST CSF
- CIS Benchmarks
- IEC 62443
Don't see your vendor? Native connectors are added continuously — the integration model is built to extend.
Platform architecture
One platform, not three point tools.
Seraxi shares one identity model, one audit trail, and one asset graph across capture, configuration, and exposure — so a finding in one product is context in the others.
Explore the platform01
Air-gap friendly
Runs fully on-prem with zero outbound internet — license, threat feeds, and AI all resolve inside your perimeter. No data leaves the appliance unless you say so.
02
Vendor-native
Speaks each device's own backup & telemetry — no fragile scraping.
03
Audit-first
Every privileged action is logged, signed, and exportable.
04
Operator-grade
Built for security ops: fast, scriptable, and honest about state.
Seraxi is built to be stood up fast and lived in — not a six-month integration project.
Deploy in a day. Operate for years.
-
01
Land
Deploy the appliance on-prem or air-gapped. No agents to roll out, no data leaving your perimeter.
-
02
Connect
Point Seraxi at your fleet and surface. Vendor-native connectors do the rest — backup, capture, discovery.
-
03
Operate
One identity model, one audit trail, one asset graph. A finding in one product is context in the others.
Frequently asked
Seraxi is an independent security-infrastructure company. We build the unglamorous, load-bearing tooling that security teams actually run their day on — with the rigor that enterprise and banking environments demand.
Does Seraxi run on-prem? +
Yes — fully. The platform is designed to run on your own appliance, including air-gapped environments. No backup, capture, or discovery data leaves your perimeter unless you explicitly export it.
Does Seraxi use AI — and where does it run? +
Yes, and on your terms. Lens uses AI to discover and assess exposed AI services and to triage vulnerabilities; Trace can answer plain-language investigation questions. Critically, the language model runs self-hosted on your own appliance — prompts and data never leave your perimeter.
Do I have to buy all three products? +
No. Trace, Keep, and Lens are standalone. Run one, two, or all three — they share one platform, so adding a product later just enriches the picture you already have.
How does it handle our existing vendors? +
Natively. Keep speaks each device's own backup path; Trace ingests your sensors; Lens maps your real external footprint. No fragile scraping or brittle screen-scraping.
How long does deployment take? +
Days, not a six-month integration project. The appliance stands up on-prem or air-gapped, vendor-native connectors do the discovery, and there are no agents to roll out across your fleet.
Does it integrate with our SIEM, SOAR, and ticketing? +
Yes. Seraxi is built to feed the stack you already run — findings, audit events, and correlated incidents are exportable into your SIEM/SOAR and ticketing workflows.
How is Seraxi licensed? +
Per product, by the scale you actually run — fleet size for Keep, capture throughput for Trace, attack surface for Lens — standalone or bundled. Talk to sales for a quote scoped to your environment.
Is it built for regulated environments? +
It's built for exactly that. Every privileged action is logged, signed, and exportable for audit — the rigor enterprise and banking environments require.
Request a demo
See Seraxi on your environment.
Book a technical walkthrough. We'll map Trace, Keep, and Lens to your fleet and show you a real backup, capture, and exposure picture — not a slide deck.
Customers
Already running Seraxi?
The customer portal holds your product downloads, installation and administration guides, release notes and support.
- Product downloads (OVA)
- Installation & admin guides
- Release notes
- Support